
What is a hex packet decoder looking at?
Most "hex packet decoder" results walk Ethernet, IP, and TCP. An E1.20 RDM dump starts 0xCC or a DUB preamble, not a MAC address.
| Dump shape | First bytes | What this site does |
|---|---|---|
| E1.20 command/response | CC 01 … | Parse 0xCC frame, checksum over body excluding checksum slots |
| Discovery Unique Branch | FE … AA … | Separate DUB path; checksum over 12 EUID bytes only |
| USB PRO widget wrap | 7E … E7 | Detect and refuse; does not unwrap |
| Ethernet / IP hex | dest MAC … 08 00 45 … | Unsupported start; not an RDM PDU |
What should I paste into an RDM packet decoder?
Paste the PDU bytes, usually starting CC 01 and ending with two checksum slots. Do not paste a pcap file.
UART printf, USB sniffer text, or a colleague paste are the usual sources. Extract the inner E1.20 body first if the capture still has Art-Net, sACN, or widget headers around it.
What is the 0xCC field map?
After 0xCC and 0x01, Message Length is one byte. Then dest UID (6), source UID (6), TN, Port ID or Response Type, message count, sub-device (2), command class, PID (2), PDL, parameter data, checksum (2).
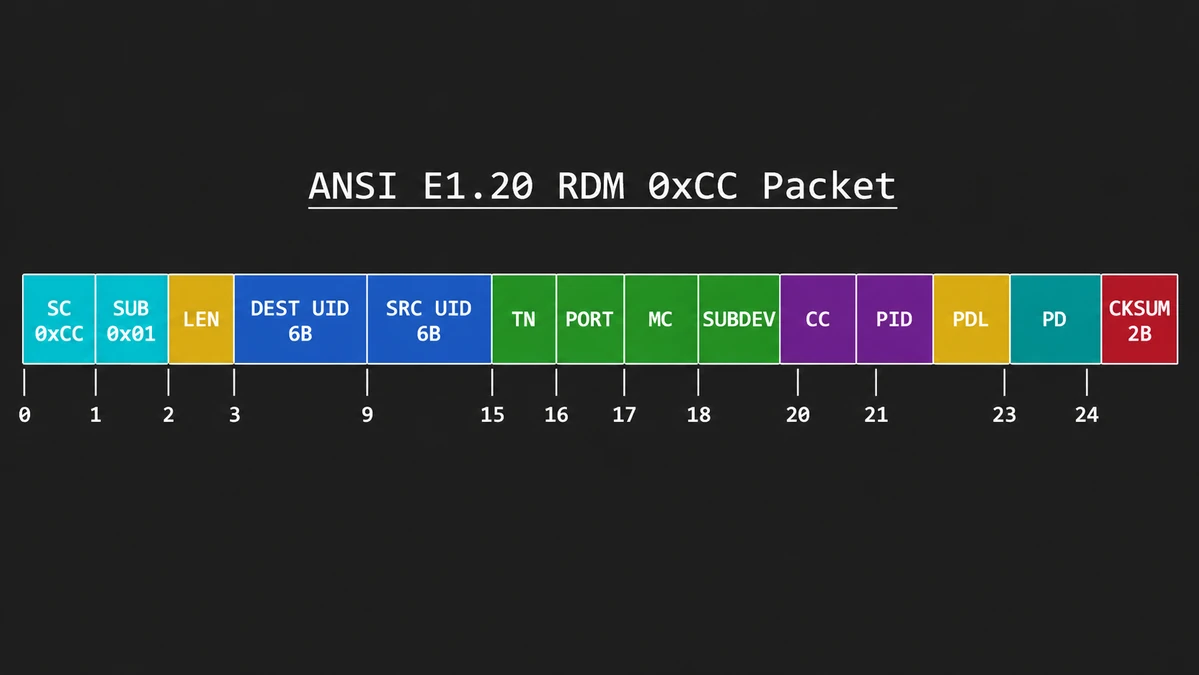
The shortest valid command is 26 bytes: Message Length 24, PDL 0. Load Example on this site is a GET IDENTIFY_DEVICE built by the same encoder the tests use:
cc 01 18 09 c8 a0 10 00 00 09 c8 01 00 cd f9 01 01 00 00 00 20 10 00 00 05 30
| Offset | Length | Field |
|---|---|---|
| 0 | 1 | Start Code 0xCC |
| 1 | 1 | Sub-Start 0x01 |
| 2 | 1 | Message Length (excludes checksum) |
| 3 | 6 | Destination UID |
| 9 | 6 | Source UID |
| 15 | 1 | Transaction number |
| 16 | 1 | Port ID or Response Type |
| 17 | 1 | Message count |
| 18 | 2 | Sub-device |
| 20 | 1 | Command class |
| 21 | 2 | PID |
| 23 | 1 | PDL |
| 24 | PDL | Parameter data |
| 24+PDL | 2 | Checksum |
How do I paste a messy hexdump?
This site strips spaces, commas, colons, hyphens, and 0x prefixes locally. It rejects odd-length or illegal characters. It does not treat an offset column as payload.
Extra bytes after a complete frame are an error. Taking only the first 26 bytes would often checksum and look like success.
How do I decode a Discovery Unique Branch dump?
Unique Branch responses are not 0xCC frames. Checksum is the additive sum of twelve EUID bytes only. Adding preamble 0xFE bytes into a handheld calculator is a common miss.
fe fe fe fe fe fe fe aa ab 5d ea dd aa f5 ba 55 aa 55 aa 55 af 57 fb 7f
How is the E1.20 checksum calculated?
The 0xCC checksum is the unsigned 16-bit sum of Start Code through Parameter Data, modulo 0x10000, excluding checksum slots. A mismatch is FAIL and prints expected versus received.
DUB sums twelve EUID bytes only. Worked GET IDENTIFY numbers from this encoder are on how to calculate an E1.20 checksum.
When is a network packet decoder the wrong tool?
Use a network decoder for Ethernet or raw IP from tcpdump. Lighting RDM on RS-485 is not that stack. Pasting CC 01 into an IP decoder will not yield UID or PID.
Why did I get QUEUED_MESSAGE instead of my GET?
ACK_TIMER means come back with GET QUEUED_MESSAGE. Believe the PID that arrived. This parser does not rewrite a 0x0050 response into the PID you hoped to see.
What should I paste next?
If the dump starts CC 01, check Message Length against size minus two, then PDL, then checksum. If it starts FE and contains AA, use the discovery path. If it starts 7E and ends E7, unwrap elsewhere.
Paste the surviving PDU in the RDM Packet Decoder Online. Keep HEX on this machine.
Frequently asked questions
Is a hex packet decoder the same as Wireshark?
No. Typical online hex decoders walk Ethernet, IP, and TCP. An E1.20 dump starts 0xCC or a DUB preamble, so an IP decoder yields a nonsense frame.
What should I paste into an RDM packet decoder?
Paste the PDU bytes, usually starting CC 01 and ending with two checksum slots. Spaces, 0x prefixes, and newlines can stay. Do not paste a pcap file.
Why does a 0x7E to 0xE7 dump fail?
That envelope is an ENTTEC USB PRO widget wrapper, not an E1.20 PDU. This decoder detects it and refuses to unwrap it so the checksum is never run on the wrong bytes.
Can leftover bytes after 26 slots still PASS?
No. A complete 0xCC frame has a defined Message Length. Extra bytes after that frame are reported. They are not silently treated as the first 26 slots.
How is the E1.20 checksum calculated?
The 0xCC checksum is the unsigned 16-bit sum of Start Code through Parameter Data, modulo 0x10000, excluding checksum slots. A miss prints expected versus received and stays FAIL.
Does decoding packets upload my dump?
Not on this site. HEX, the field table, and JSON copy or download stay in the browser. There is no decode API.